
Overview
The Mend container image registry scanning solution can integrate with your private ECR using your provided access and secret keys.
Getting it done
Prerequisites before you scan ECR with Mend Container
-
Your Mend user must be an organization administrator.
-
The Amazon IAM user that owns the access and secret keys provided to Mend must have an IAM policy attached that grants the required ECR actions on all registry resources (
"Resource": "*"). Restricting the policy to specific repositories is not supported. See the Amazon ECR setup section below for the full policy. -
Images up to 4GB in size are supported.
Amazon ECR setup
Step 1: Create the access and secret keys in AWS:
-
Navigate to your AWS Management Console and open the IAM console.
-
Select Users and click on the user that will be used for the integration.
-
Navigate to the Security Credentials tab → Access keys section and click on Create access key.
-
Once you finish, keep the access and secret keys on hand for the integration.
Step 2: Create the policy in AWS:
-
Navigate to your AWS Management Console and open the IAM console.
-
In the navigation pane on the left, select Policies and click Create.
-
Use the following policy. The
Resourceelement must be"*":
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Effect": "Allow",
      "Action": [
        "ecr:GetAuthorizationToken",
        "ecr:BatchCheckLayerAvailability",
        "ecr:BatchGetImage",
        "ecr:DescribeRepositories",
        "ecr:GetDownloadUrlForLayer",
        "ecr:GetRepositoryPolicy",
        "ecr:ListImages",
        "ecr:ListTagsForResource",
        "ecr:DescribeImages"
      ],
      "Resource": "*"
    }
  ]
}
Why "Resource": "*" is required: When testing the connection and before every scan, Mend first lists all repositories in your ECR registry, and only then applies the Include/Exclude filters you define in the setup wizard to decide which repositories and tags to scan. Scoping the Resource element to specific repositories (for example, arn:aws:ecr:REGION:ACCOUNT_ID:repository/my-repo/*) is not supported: the connectivity check fails with an AccessDenied error on ecr:DescribeRepositories, and scans will fail. To limit which repositories Mend scans, use the Include/Exclude filters in Step 4 - Pull and Scan Inventory instead.
Step 3: Attach the policy in AWS:
-
Navigate to your AWS Management Console and open the IAM console.
-
Select Users and click on the user that owns the access and secret keys generated in Step 1.
-
Navigate to the Permissions tab and click on Add permissions → Add permissions.
-
For the Permissions options, select Attach policies directly.
-
Select the created policy from Step 2 and click on Next.
-
Click on Add Permissions to attach the policy to the user.
Set up your private ECR configuration via the Mend Platform UI
-
In the Mend Platform UI, navigate to
-
Scroll down to the ‘Registries’ section and click ‘Amazon ECR’ to open the setup wizard.
The Setup Wizard
Step 1 - General Details
Fill in the General Details fields:
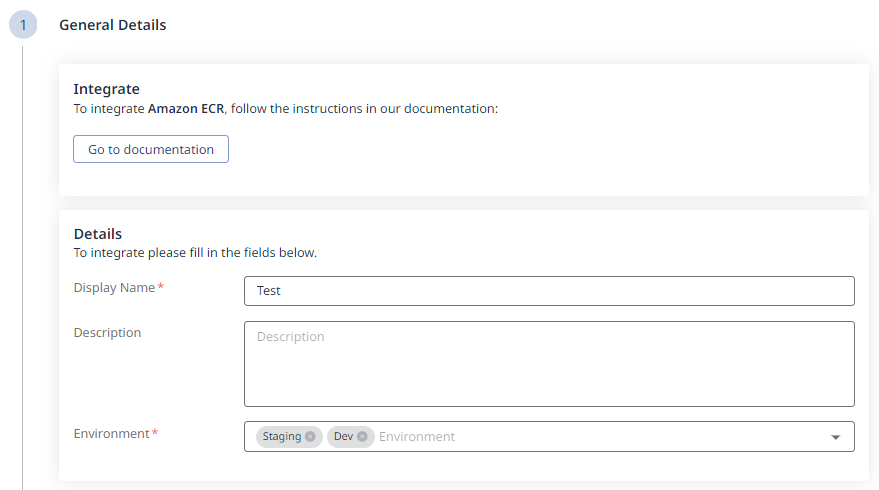
a. Display Name
b. Description (optional)
c. Environment (multi-selection is supported)
Click the 
Step 2 - Authentication
Fill in the required Authentication information:
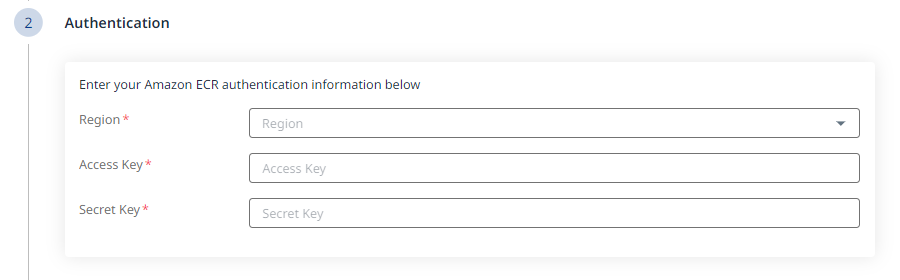
a. Region
b. Access Key
c. Secret Key
Click the
Step 3 - Configuration
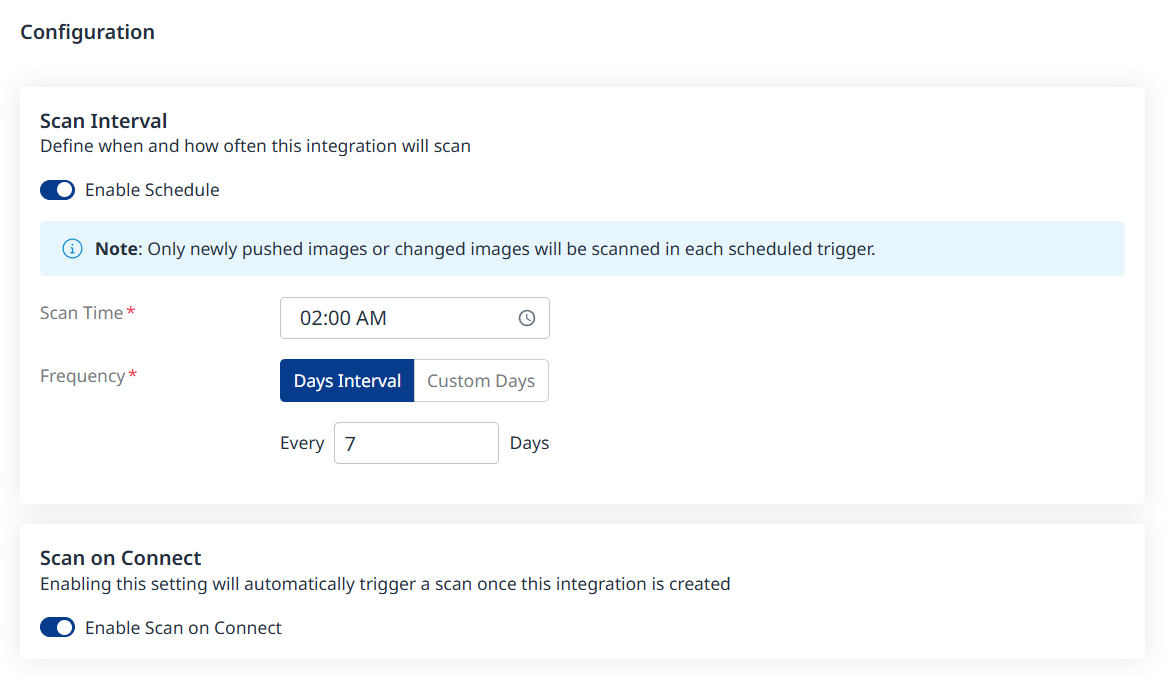
Fill in the Configuration information to define your scan schedule:
-
Enable Schedule - Toggle off to disable scheduling.
-
Scan Time
-
Frequency
-
Scan on Connect - While toggled on, it means a scan will be triggered automatically once the integration setup is completed.
Scheduling image registry scans is crucial for maintaining the security and integrity of your container images. By default, a scan interval of 7 days will be applied. You can change the scan interval in 1-day increments or select specific days of the week when you wish for scans to be executed.
Note: After the first scan (in which the latest 10 tags are scanned), in every scheduled scan only newly pushed images from the registry or changed images will be scanned. This is because vulnerability and package updates occur automatically in an asynchronous manner, keeping the security information up-to-date without requiring new scans.
Click the
Step 4 - Pull and Scan Inventory
Define which repositories and tags should be pulled and scanned using include/exclude filters:
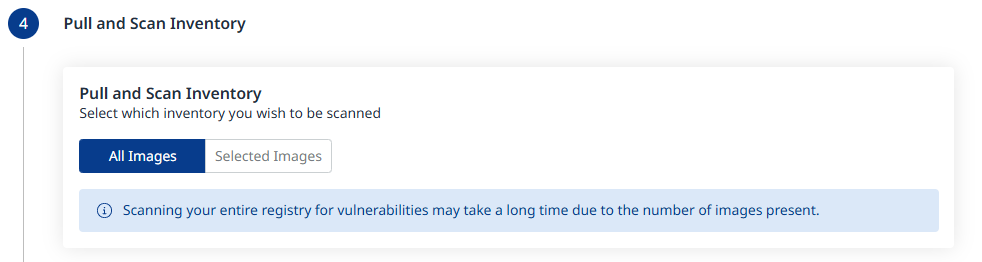
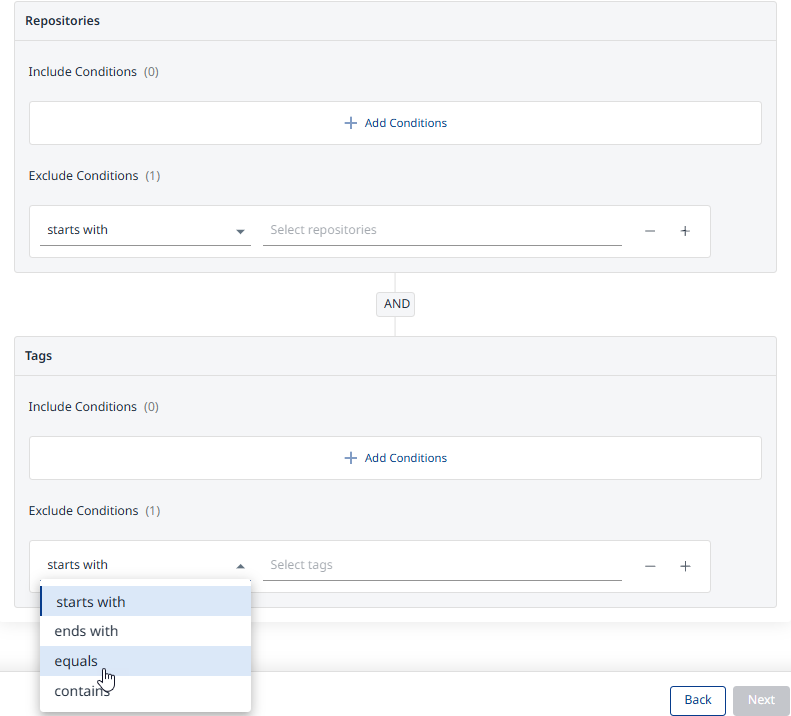
All Images will be the default. When changing this to Selected Images as shown below, click Add Conditions to add Include and/or Exclude conditions, for both Repositories and Tags.
Note: These filters control which repositories and tags Mend scans, not which repositories Mend can access. Mend first lists all repositories in the registry and then applies the Include/Exclude filters, so the IAM policy must still grant access to all resources ("Resource": "*"). See Amazon ECR setup above.
Step 5 - Summary
In this step, the summary of your input from steps 1-3 will be displayed. You can go back to the previous screens of the wizard to make changes, by clicking the ‘Back’ button at the bottom right corner of the screen. If you wish to confirm your configuration and add your registry, click the ‘Done’ button:
A Registry Added Successfully message will pop-up at the bottom-left corner of the user interface once the integration credentials and configuration have been verified:
Note: Before adding your registry, a connectivity check will be performed automatically, to ensure the credentials are valid and the registry is accessible for the integration.
Reference
Private ECR parameters
|
Parameter |
Description |
|
Display Name |
Type the name of your registry. This will be displayed in the Integrations dashboard. |
|
Description |
Optional. Provide any text. We recommend providing information that will help you remember the integration and/or the relevant registry. |
|
Region |
Select the AWS region where your ECR is hosted. The region options are:
|
|
Environment |
Label your ECR with the environments types that you manage (multiple options can be selected). The environment options are:
|
|
Access Key |
Provide your ECR access Key. |
|
Secret Key |
Provide your ECR secret Key. |
Amazon ECR resources
Visit Amazon’s documentation below for more information on the topics related to the Mend private ECR integration: